See More
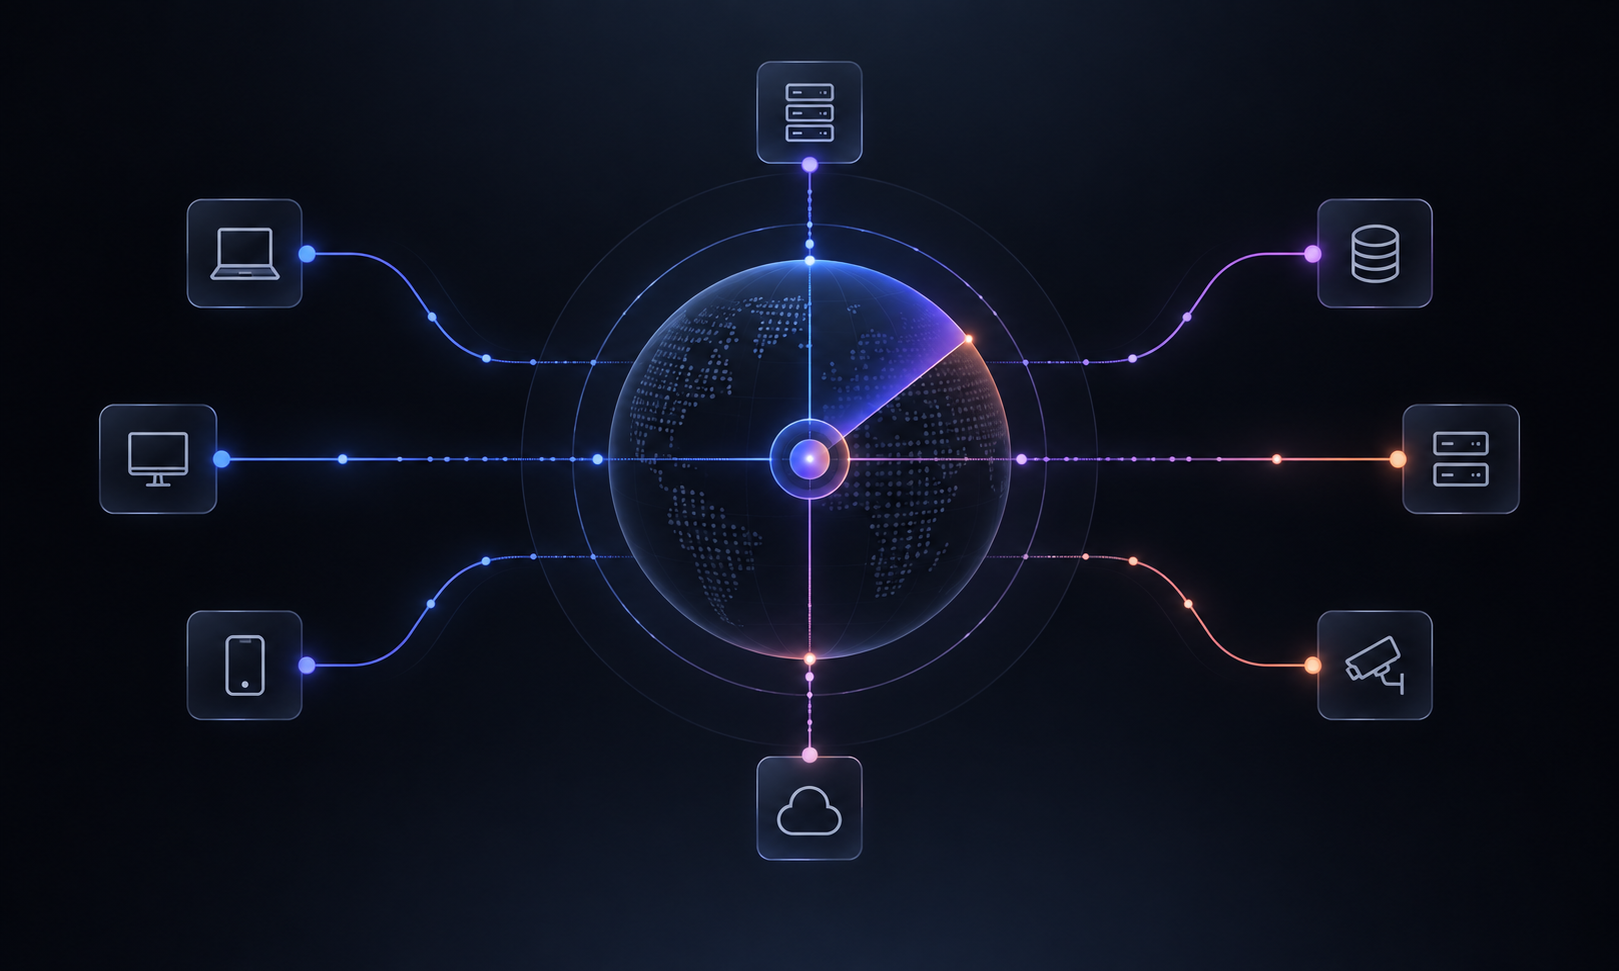
Continuous visibility across north-south and east-west traffic, including unmanaged assets.
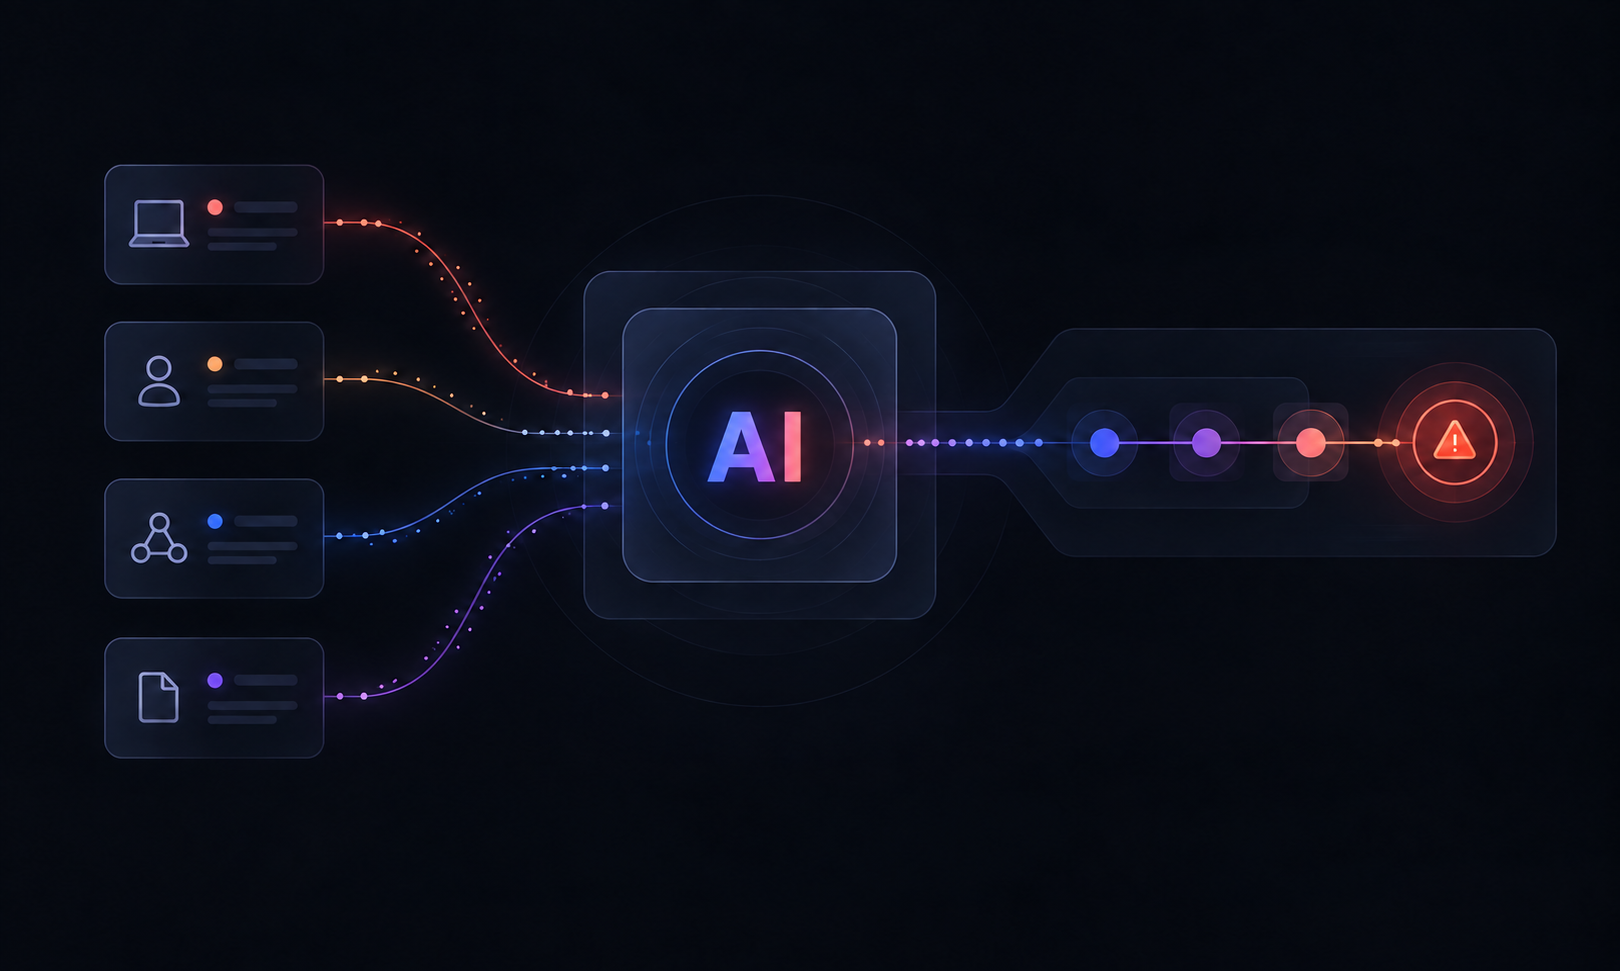
AI-NDR continuously analyzes network traffic and behavior, connecting weak signals across hosts, sessions, protocols, files, and threat intelligence to reveal the full attack story.
Continuous visibility across north-south and east-west traffic, including unmanaged assets.
Find compromised hosts, lateral movement, C2, malware, and unknown threats before they spread.
Correlate related events across hosts, sessions, protocols, files, and time.
Contain malicious activity through firewall, SIEM, SOAR, and EDR integrations.
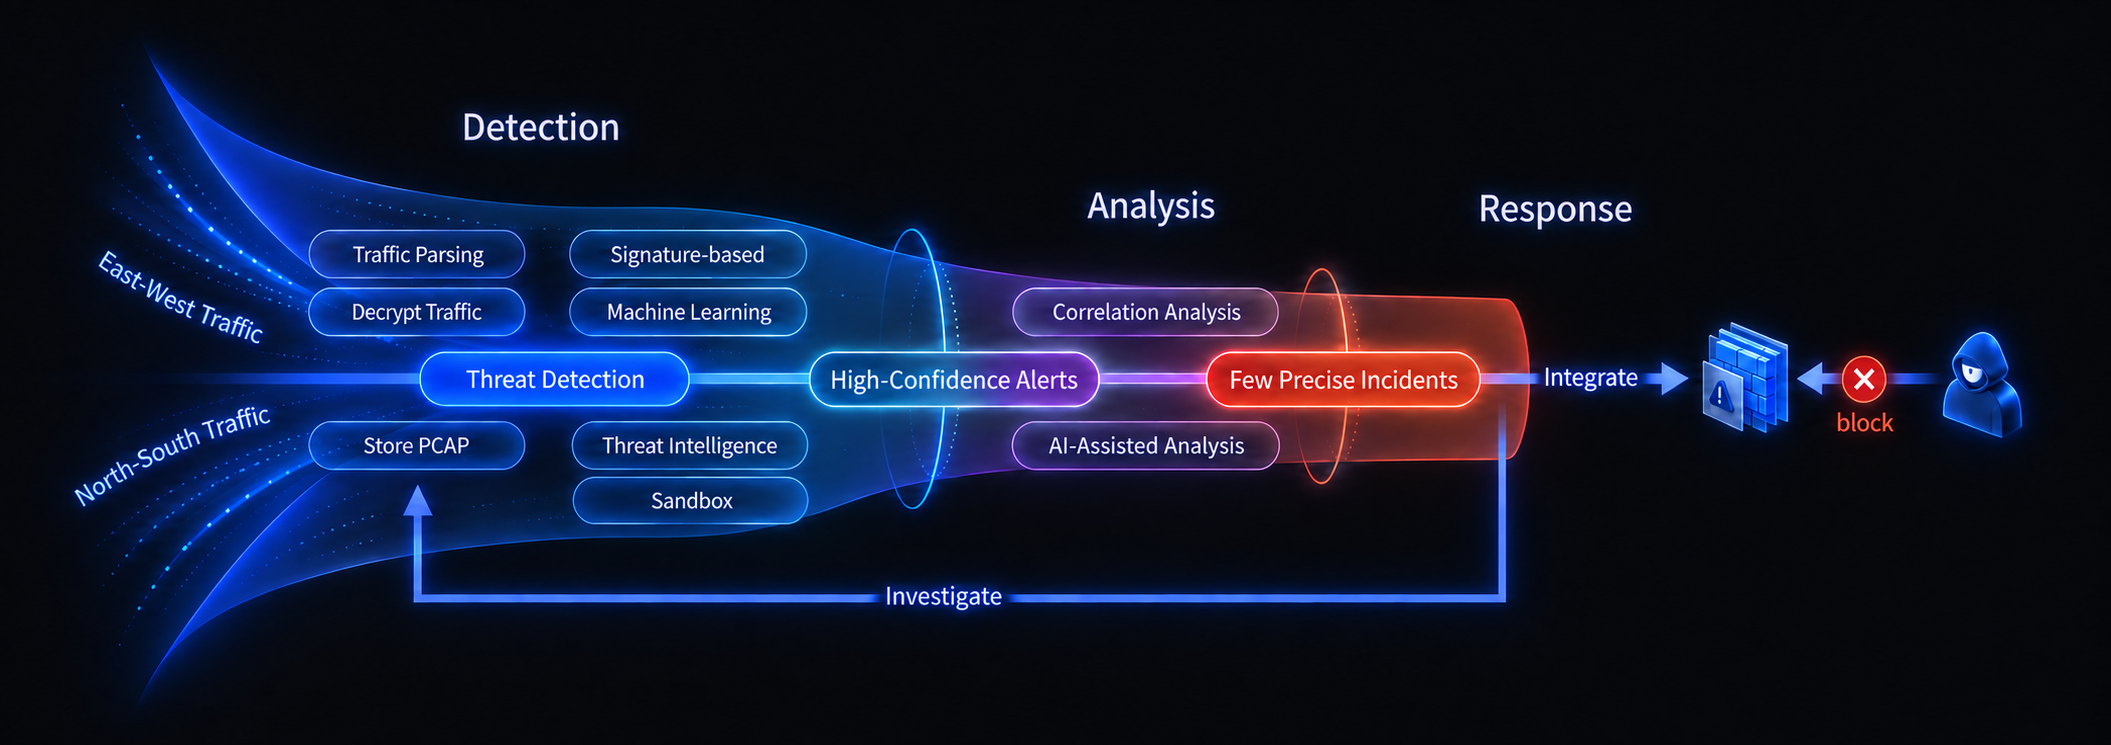
Multiple detection methods work together, so teams are not dependent on signatures or isolated indicators.
Continuously analyze sessions, protocols, assets, files, and north-south + east-west communication.
Identify C2 behavior, suspicious domains, covert channels, exploit behavior, and malware communications.
Find brute-force activity, unusual internal communication, cryptomining, remote access, and service abuse.
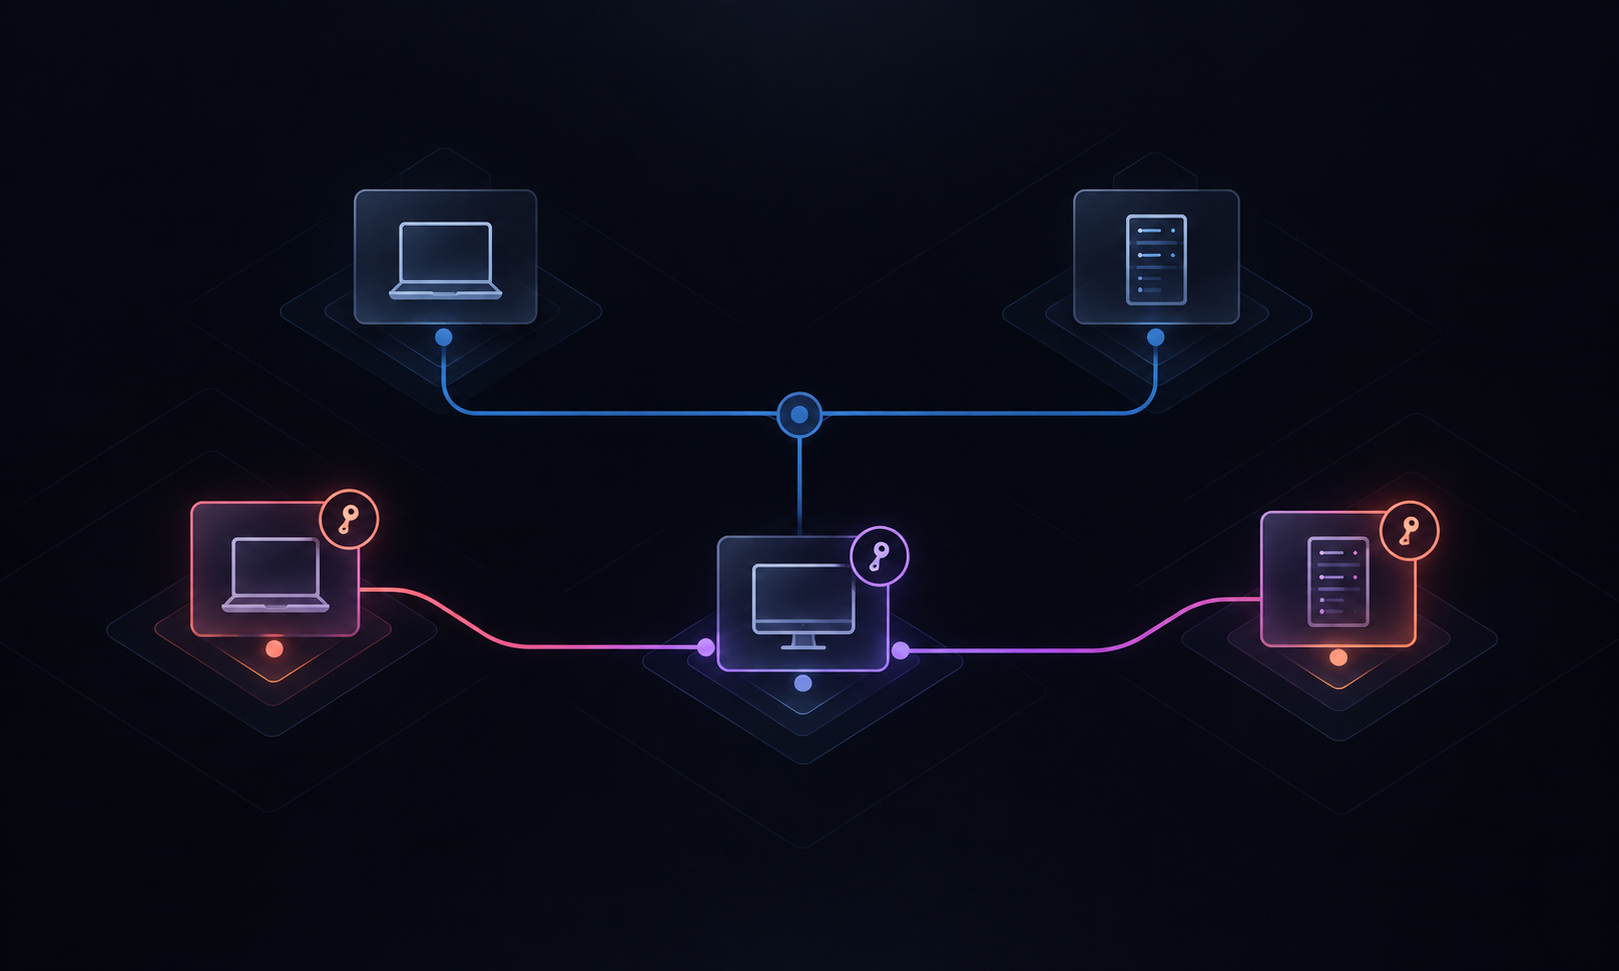
Track credential abuse, SMB activity, internal reconnaissance, exploitation, and remote access between systems.
Combine threat intelligence, static analysis, file extraction, and dynamic sandbox execution.
Connect weak signals across entities and time to reconstruct the attack chain and prioritize true risk.
Deploy out of band using mirrored traffic. Gain network truth without disrupting production applications.
Analyze network activity without installing agents on every monitored asset.
Use SPAN, TAP, or mirrored traffic to keep the production path unchanged.
Support IPv4 + IPv6, distributed sensors, centralized analysis, and hybrid environments.
See the attack. Understand the behavior. Stop the threat.
Book a Demo